

100% Pass Top-selling NSE5_FCT-6.2 Exams - New 2021 Fortinet Pratice Exam
NSE 5 Network Security Analyst Dumps NSE5_FCT-6.2 Exam for Full Questions - Exam Study Guide
NEW QUESTION 13
Refer to the exhibit.
Based on the FortiClient logs shown in the exhibit which endpoint profile policy is currently applied to the FortiClient endpoint from the EMS server?
- A. Default configuration policy
- B. WIK-EKVK3EA3S71
- C. Default
- D. Fortinet-Training
Answer: C
NEW QUESTION 14
What is the function of the quick scan option on FortiClient?
- A. It scans executable files. DLLs, and drivers that are currently running, for threats.
- B. It scans programs and drivers that are currently running for threats
- C. It allows users to select a specific file folder on your local hard disk drive (HDD), to scan for threats
- D. It performs a full system scan including all files, executable files, DLLs, and drivers for threats.
Answer: B
NEW QUESTION 15
Which statement about FortiClient comprehensive endpoint protection is true?
- A. It helps to safeguard systems from data loss.
- B. lt helps to safeguard systems from advanced security threats, such as malware.
- C. It helps to safeguard systems from DDoS.
- D. It helps to safeguard systems from email spam
Answer: B
NEW QUESTION 16
Refer to the exhibit.
Based on the settings shown in the exhibit what action will FortiClient take when it detects that a user is trying to download an infected file?
- A. Quarantines the infected files and logs all access attempts
- B. Blocks the infected files as it is downloading
- C. Allows the infected file to download without scan
- D. Sends the infected file to FortiGuard for analysis
Answer: C
NEW QUESTION 17
In a FortiSandbox integration, what does the remediation option do?
- A. Deny access to a file when it sees no results
- B. Alert and notify only
- C. Exclude specified files
- D. Wait for FortiSandbox results before allowing files
Answer: D
NEW QUESTION 18
When site categories are disabled on FortiClient webfilter and AV (malicious websites), which feature protects the endpoint?
- A. FortiSandbox URL list
- B. Web Exclusion list
- C. Block malicious websites on Antivirus
- D. Endpoint host file
Answer: B
NEW QUESTION 19
An administrator installs FortiClient on Windows Server.
What is the default behavior of real-time protection control?
- A. Real-time protection must update AV signature database
- B. Real-time protection sends malicious files to FortiSandbox when the file is not detected locally
- C. Real-time protection is disabled
- D. Real-time protection must update the signature database from FortiSandbox
Answer: C
NEW QUESTION 20
An administrator is required to maintain a software inventory on the endpoints. without showing the feature on the FortiClient dashboard What must the administrator do to achieve this requirement?
- A. The administrator must click the hide icon on the vulnerability scan tab
- B. The administrator must not select the vulnerability scan feature in the deployment package.
- C. The administrator must use default endpoint profile
- D. The administrator must select the vulnerability scan feature in the deployment package, but disable the feature on the endpoint profile
Answer: D
NEW QUESTION 21
Refer to the exhibits.

Based on the FortiGate Security Fabric settings shown in the exhibits, what must an administrator do on the EMS server to successfully quarantine an endpoint. when it is detected as a compromised host (loC)?
- A. The administrator must enable FQDN on EMS.
- B. The administrator must enable SSH access to EMS.
- C. The administrator must enable remote HTTPS access to EMS.
- D. The administrator must authorize FortiGate on FortiAnalyzer.
Answer: C
NEW QUESTION 22
Which two third-party tools can an administrator use to deploy FortiClient? (Choose two )
- A. MSI Editor
- B. Microsoft SCCM
- C. Microsoft Active Directory GPO
- D. Microsoft Windows Installer
Answer: B,C
NEW QUESTION 23
Refer to the exhibit.
Based on the CLI output from FortiGate. which statement is true?
- A. FortiGate is configured with local user group
- B. FortiGate is configured to pull user groups from FortiClient EMS
- C. FortiGate is configured to pull user groups from FortiAuthenticator
- D. FortiGate is configured to pull user groups from AD Server.
Answer: B
NEW QUESTION 24
Refer to the exhibit.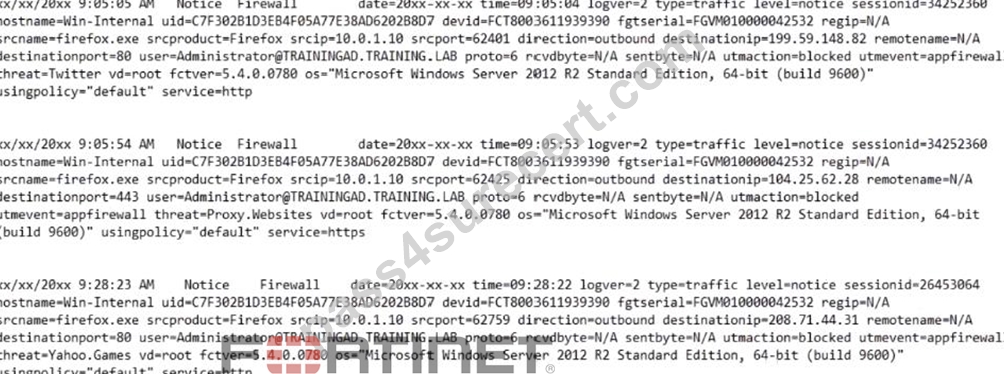
Based on the FortiClient logs shown in the exhibit which application is blocked by the application firewall?
- A. Internet Explorer
- B. Firefox
- C. Facebook
- D. Twitter
Answer: B
NEW QUESTION 25
......
Authentic Best resources for NSE5_FCT-6.2 Online Practice Exam: https://www.pass4surecert.com/Fortinet/NSE5_FCT-6.2-practice-exam-dumps.html